Mobile app vulnerability report and checklist
Every app store release hands attackers a copy of your app
Once it’s out there, they can take it apart, modify it and run it on a compromised device.
Our example report shows where published apps are exposed before Ditto Protect is deployed, and the protection they enjoy after. Our checklist helps you assess where your app stands today.
What poor app protection gives away
What ships with your app, ships to attackers
They don't need to breach anything to start. What they find inside the package decides how much effort an attack takes.

They map your estate
Backend hosts, storage buckets and service names sit in plain view, including ones your team thought were private.

They find your keys
Embedded credentials let them call your APIs as if they were your app. Permissive certificate handling lets them read and replay traffic on a shared network.

They read what’s left behind
Session caches and temp files stay on the device. A lost or rooted handset becomes a data incident.
Every endpoint, key and class name left readable gives an attacker a head start.

Leave the package unprotected and it describes your estate to anyone who asks.
-
Protect one release without building protection into your pipeline, and the next release reopens the gap.

Rely on a lab test alone, and you get a two-week snapshot that lists findings without showing how they were found. Gaps pass sign-off, then resurface in a later release.

Switch protection on. See what an attacker loses.
Choose from the example apps in different industries below. We assessed each one twice: as released, and with Ditto Protect. See the results and then get the detailed report.
Northwind Banking*
Android · v4.2.0Everyday current accounts, card controls and payments for four million retail customers.
Retail banking · illustrative example
Payment flows exposed without adequate transport security
Transport-layer weaknesses in checkout and transfer flows let an attacker on the same network read payment data in transit.
TLS configuration allows interception of banking traffic
Permissive certificate handling makes man-in-the-middle interception realistic on any untrusted network.
Backend service endpoints discoverable and under-protected
Internal API hosts and storage buckets were readable straight from the package, handing attackers a map of your estate.
Some local caches still hold recoverable session data
Cached session artefacts remain on rooted devices; runtime protection narrows the window but cannot remove the files.
Legacy crypto calls remain inside third-party libraries
Two bundled SDKs still call deprecated ciphers that cannot be rewritten without a vendor update.
That's the summary. The detailed report goes further.
For each finding: what we found, why it matters to a retail bank, what's left after protection, and the six controls that keep it closed.
Larkspur Pay*
Android · v3.1.4Instant transfers, virtual cards and expense controls for small business teams.
Payments and fintech · illustrative example
Gateway API keys shipped inside the app binary
Live payment-gateway keys sat in plain strings, letting anyone replay authenticated calls from outside your app.
Card entry screens open to overlay attacks
Nothing stopped a malicious app from drawing over the card-entry flow to harvest details as they were typed.
App runs happily after being repackaged
Modified builds passed no integrity check, so cloned wallets could be distributed outside the official stores.
Transaction history cached longer than needed
Statement data persisted in local storage after sign-out; only a fraction survives once storage is hardened.
Analytics SDK still reads device identifiers
A vendor SDK collects hardware identifiers under its own consent flow, outside the protected boundary.
This is the summary. The detailed report goes further.
For each finding: what we found, why it matters to a payments business, what's left after protection, and the six controls that keep it closed.
Ashgrove Insure*
Android · v2.8.2Motor and home cover with photo-based claims assessment and instant quotes.
Insurance · illustrative example
Claim documents left readable on the device
Uploaded photographs and claim PDFs were written to shared storage where any other app could read them.
Claims traffic sent over downgradeable connections
Fallback to cleartext was permitted, so an attacker could force claims submissions onto an unencrypted channel.
Document storage buckets addressable from the app
Bucket names and region hints in the package allowed direct enumeration of stored claim evidence.
Some diagnostic logs still capture policy numbers
Verbose logging in the offline quote module records policy references that reach your crash reporter.
Legacy key derivation in the offline quote module
An older derivation routine remains for backwards compatibility with quotes saved on previous versions.
This is the summary. The detailed report goes further.
For each finding: what we found, why it matters to an insurer, what's left after protection, and the six controls that keep it closed.
Vantage Play*
Android · v6.0.7Live tables and tournaments with real-money balances and instant payouts.
Gaming and betting · illustrative example
Game client can be modified without detection
Balance and odds logic could be patched in a repackaged build and still connect to your live tables.
Hooking frameworks attach to the running game
Common instrumentation tools attached at runtime, exposing every in-game call and wallet operation.
Server tokens embedded in the shipped build
Static service tokens in the binary allowed table state to be queried without an authenticated session.
Play from emulators remains partly possible
Hardened checks block known emulators, but bespoke virtual devices can still reach the lobby.
Ad SDK still fingerprints the device
The bundled ad network builds its own device signature outside the protected runtime.
This is the summary. The detailed report goes further.
For each finding: what we found, why it matters to a gaming operator, what's left after protection, and the six controls that keep it closed.
Meridian Stay*
Android · v5.4.1Booking, mobile room keys and contactless check-in across 240 properties.
Travel and hospitality · illustrative example
Door-key service credentials sat in the package
Credentials for the mobile key service were extractable, putting room access logic within reach of an attacker.
Booking traffic interceptable on shared wifi
Weak certificate validation made guest bookings readable on exactly the networks guests use most.
Reservation APIs enumerable from the client
Endpoint patterns in the binary allowed reservation identifiers to be walked without authentication.
Guest profile cache persists after sign-out
Name and stay history remain in an encrypted local cache until the next launch clears it.
Loyalty identifiers still appear in crash reports
Membership numbers are attached to diagnostic payloads handled by your third-party reporter.
This is the summary. The detailed report goes further.
For each finding: what we found, why it matters to a hotel group, what's left after protection, and the six controls that keep it closed.
Cardia Health*
Android · v1.9.6Appointments, repeat prescriptions and remote cardiac monitoring for patients at home.
Healthcare · illustrative example
Patient records written to unprotected storage
Monitoring readings and prescription history were cached in cleartext on the device filesystem.
Health data encrypted with deprecated ciphers
Records at rest used algorithms considered broken, so encryption offered little practical protection.
Clinical backend endpoints exposed in the binary
Hostnames for the clinical record service were readable, exposing internal infrastructure to probing.
Monitoring SDK still transmits device metadata
The device vendor SDK reports hardware telemetry through its own channel, outside the protected boundary.
Appointment cache readable on rooted devices
A small appointment cache stays accessible where the device itself is already compromised.
This is the summary. The detailed report goes further.
For each finding: what we found, why it matters to a healthcare provider, what's left after protection, and the six controls that keep it closed.
Inside the report
Every gap we found, and what it takes to close them.
Know where you stand before an external test or regulator tells you. The report sets out the gaps we typically find in apps like yours, with a management summary and the detail engineers and auditors need.


A summary in plain English
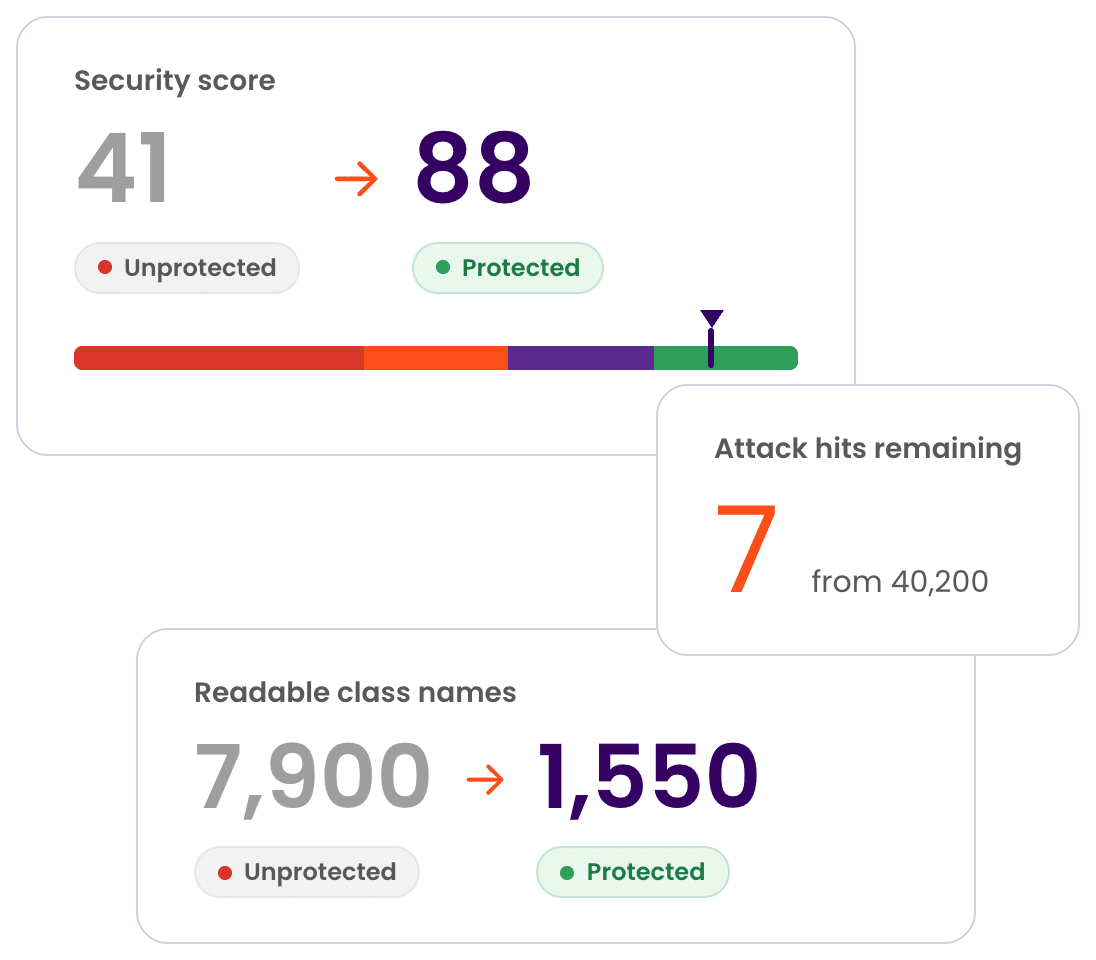
The app's exposure score and attack surface before and after Ditto Protect, and what the change means for a business in your industry.
-
Every finding in full
Organised by exposure area: what we found, what's left once protection is applied and the fixes that need code or vendor changes.
-
The controls to evidence each release
Turn each finding into a check for your own app: a control checklist for every exposure area, with a sign-off record so the evidence is in hand before anyone asks for it.


Request the example report
Get the detailed breakdown and checklist
Tell us where to send it. The report arrives in your inbox within a few minutes.
Maha Bahou
CEO, JoPACC
"Ditto's cryptographically secured communication protocol protects our financial digital identity platform, ensuring trusted data exchange between data subjects and the platform while protecting sensitive information."